Empowering Cyber Resilience through GRC-Oriented Cyberlaw Solutions
It is not always the technology infrastructure itself that keeps an organisation’s information secure. Weak cybersecurity governance, the lack of continuous vulnerability assessments, inadequate data classification, insufficient systems auditing, and inadequate oversight of system administrators are among the major contributors to a vulnerable cyber environment.
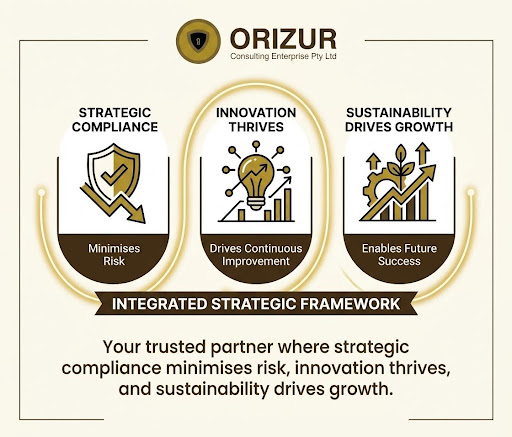
We develop authentic, regulatory-aligned cyberlaw solutions to protect our clients’ assets, enhance operational efficiency, and drive financial stability, whilst minimising regulatory and reputational risks.
Proprietary Methodologies & Frameworks
At the core of our strategic framework are two flagship methodologies which Orizur employs to operationalise compliance across diverse sectors using authentic, proprietary, regulatory-aligned implementation models:
Data Privacy & Cybersecurity Governance Technique
A comprehensive, four-tier assessment model spanning Data Classification, System Specification Vetting, Access Accreditation, and Infrastructure Auditing.
Enterprise Risk and Compliance Framework
Grounded in our GRC approach, this unique framework integrates cybersecurity, digital transformation management, ICT contract management, and sustainability to achieve business–IT alignment, improve compliance and security, increase cost-effectiveness, and enhance good governance and accountability.
Through these regulatory-aligned cyberlaw solutions, Orizur enables clients to understand their complete cyber environment, track and demonstrate compliance and risk resilience, and maintain a cyber-secure environment holistically and cost-effectively.
Client Benefits
The benefits our clients derive from these comprehensive cyberlaw solutions include: